
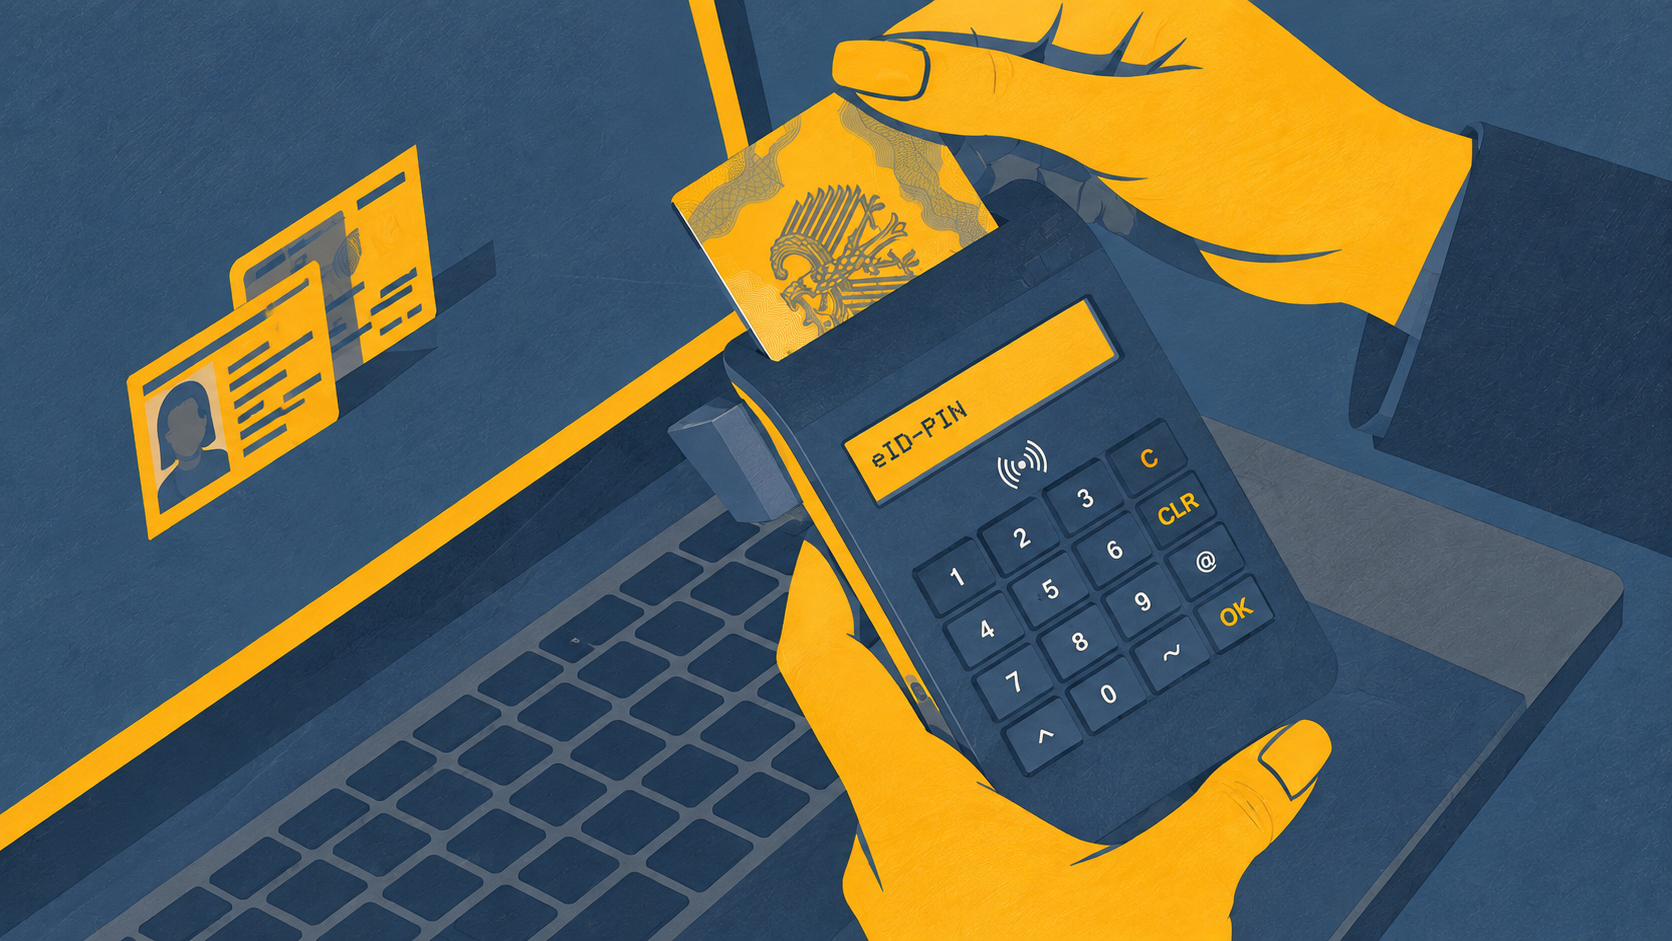
Identity verification technology provider Sumsub has introduced software intended to control what AI agents can access within corporate systems and to require human authorisation for selected sensitive activities. The KYA Module for MCP expands the company’s Know Your Agent framework, with initial integration support focused on Amazon Bedrock AgentCore Gateway.
The module is designed to sit between an automated agent and data sources or applications to which it has been connected. Sumsub says requests can be checked against configurable rules before information is released or an action proceeds, allowing organisations to set restrictions according to the task and sensitivity of the material involved.
The Model Context Protocol provides a way for AI applications to interact with external systems and tools. Such connections can make software more useful, but also give it access to documents, customer records and functions capable of changing information or triggering transactions.
Traditional access permissions may grant an application broad rights that exceed what it needs for an individual task. A system asked to prepare a summary could potentially see confidential information unrelated to that work. Restricting the information returned may reduce unnecessary exposure, although the quality of filtering depends on how policies and integrations are configured.
Sumsub says the new module can remove personal and other sensitive information from requests reaching an AI agent. It also records activity so businesses can examine what an automated system requested and the actions associated with its work.
For selected higher-risk operations, the platform can trigger liveness or identity verification involving a human. Examples include requests to access restricted files or approve financial activity above a defined threshold. The controls seek to ensure consequential actions are linked to accountable users rather than an agent acting without additional authorisation.
Such safeguards are only useful where responsibilities are clearly defined. A company must decide who can approve particular activities, which systems can be connected and what should happen if a request fails a check. A poorly designed rule may interrupt legitimate work, while an overly permissive one could leave sensitive data exposed.
Sumsub introduced an earlier agent verification capability in January and additional functionality in June. The October release extends its offering to a broader access-control role. It should not be described as a wholly new identity security market or evidence that the company has already prevented a specified number of attacks.
Audit logs can help investigators reconstruct activity after an error or incident, but their reliability depends on what events are captured and whether records can be protected from alteration. Integrating logs with existing security monitoring may be as important as generating them in the first place.
The launch also highlights the difference between identifying the person responsible for an agent and ensuring every action is appropriate. Verified ownership does not make automated decisions accurate, and humans may still approve unsuitable requests unless they have enough information to assess the risks.
Sumsub’s product documentation initially names Amazon Bedrock AgentCore Gateway as the supported environment, with other MCP gateways expected later. The announcement therefore does not establish universal compatibility with every AI agent or tool connection currently available.
Human verification can be useful for exceptional actions but creates a new dependency on the availability and judgement of authorised employees. Organisations will need contingency arrangements for urgent activity and rules governing delegated approvals, especially where agents operate outside ordinary working hours. An unexplained interruption could be costly even when a security policy is technically enforced as designed.
Data filtering must also be considered alongside privacy law and the existing controls within source applications. Removing selected information before it reaches an agent does not establish that all processing is lawful or that sensitive records cannot be exposed through another route. Effective deployment requires a broader understanding of system boundaries, logging, permissions and information retention.
Organisations considering adoption will need to assess integration, security assurance and policy management alongside potential productivity gains. The usefulness of governed AI depends on creating boundaries that are technically enforceable and commercially proportionate to the tasks delegated.
You must be logged in to post a comment.