Semperis has expanded its Lightning security platform to help businesses identify and respond to threats involving employee accounts, privileged users, service identities, and autonomous AI agents across corporate IT environments.
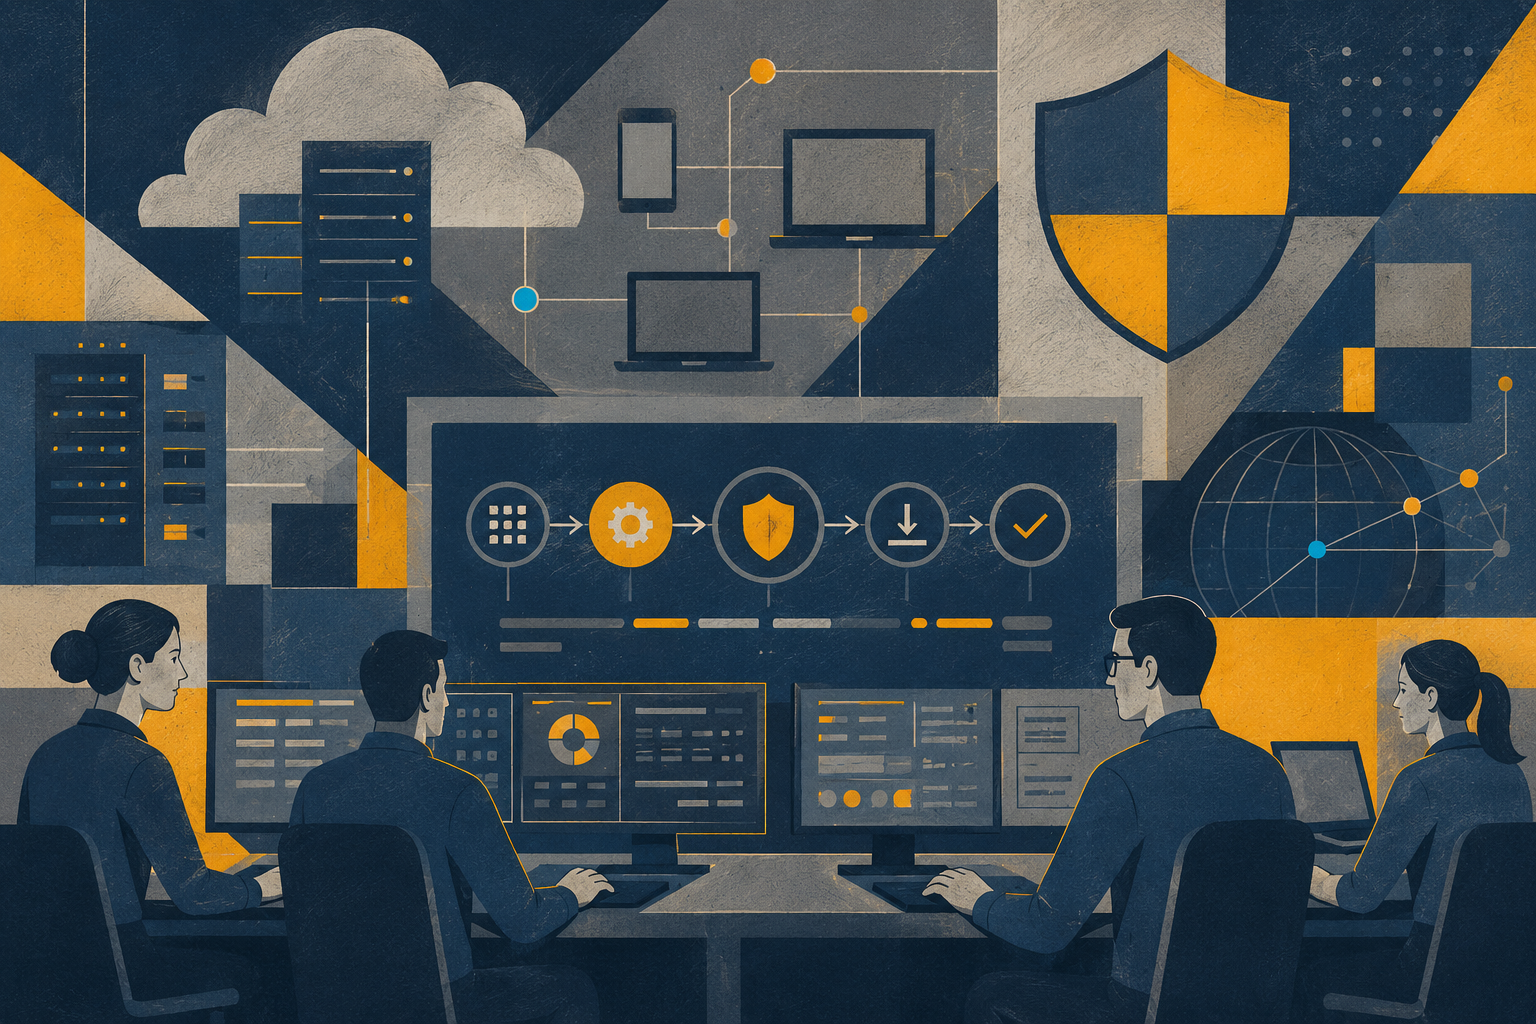
The latest capabilities bring identity exposure management, attack-path analysis, account discovery, suspicious activity detection, and remediation into a common platform covering Microsoft Active Directory, Microsoft Entra ID, and Okta.
Semperis is addressing the increasing complexity of access management as organisations introduce automated systems capable of retrieving information and performing activities across multiple applications.
These AI agents often operate using non-human identities, such as service accounts or other credentials that allow software to access business resources without a person signing in for every transaction.
Permissions assigned to those identities can become a security concern if they are broader than necessary or provide unexpected routes into sensitive systems.
The expanded Lightning platform is designed to identify those relationships and help security teams assess which exposures could permit unauthorised access to critical infrastructure.
Semperis announced the latest release on 17 November. Lightning had already been introduced earlier in 2026, with the new announcement detailing the consolidated identity security and response capabilities.
Mapping access across business systems —
The platform uses a catalogue of more than 300 security indicators to assess identity infrastructure for potential exposures involving human and non-human accounts.
It assigns risk scores to findings and allows security teams to investigate them through a shared workflow.
A live identity graph maps relationships between accounts, permissions, and important resources, including routes leading to domain administrators and other privileged accounts.
Attack-path analysis helps establish whether several individually manageable access weaknesses could combine to create a route towards a critical system.
That context can inform the order in which organisations address exposures, particularly where security teams face more findings than they can investigate immediately.
Lightning also provides a searchable inventory covering human identities, automated accounts, and agentic identities discovered within supported environments.
This is relevant where accounts created for applications or automated processes do not appear in conventional employee access reviews.
As organisations introduce AI agents into finance, operations, customer service, and IT administration, their security teams need to understand what those systems are permitted to access and which other services depend on their credentials.
The platform is designed to connect those assessments with security monitoring and corrective action.
Combining detection with recovery —
Semperis has incorporated detection capabilities for suspicious changes and authentication activity in Active Directory and Entra ID.
These include monitoring involving Kerberos and NTLM logons, alongside rule templates and generative assistance intended to support investigations.
Security teams can use the findings to identify changes requiring attention and examine their relationship to sensitive accounts or resources.
Semperis also provides capabilities intended to reverse risky directory changes and support the recovery of affected identity systems.
Those recovery functions are important because identity services underpin access to numerous other business applications. Disruption to a directory or authentication service can prevent employees and automated processes from accessing systems they require.
Alex Weinert, chief product officer at Semperis, said the company’s approach combines information about identity exposure, access relationships, suspicious changes, and remediation within one platform.
The integration is intended to reduce the need to move between separate tools when investigating a potential identity compromise.
Semperis has not published independently verified figures demonstrating that the expanded platform reduces incident response times by a particular amount.
Actual outcomes will depend on customers’ identity architecture, monitoring arrangements, security policies, and response procedures.
The latest Lightning release extends Semperis’s established identity security offering to address the additional access relationships created as businesses deploy more automated and AI-driven processes.